AI Agent Deployment in Production: Latency, Prompt Drift, Cost & Security
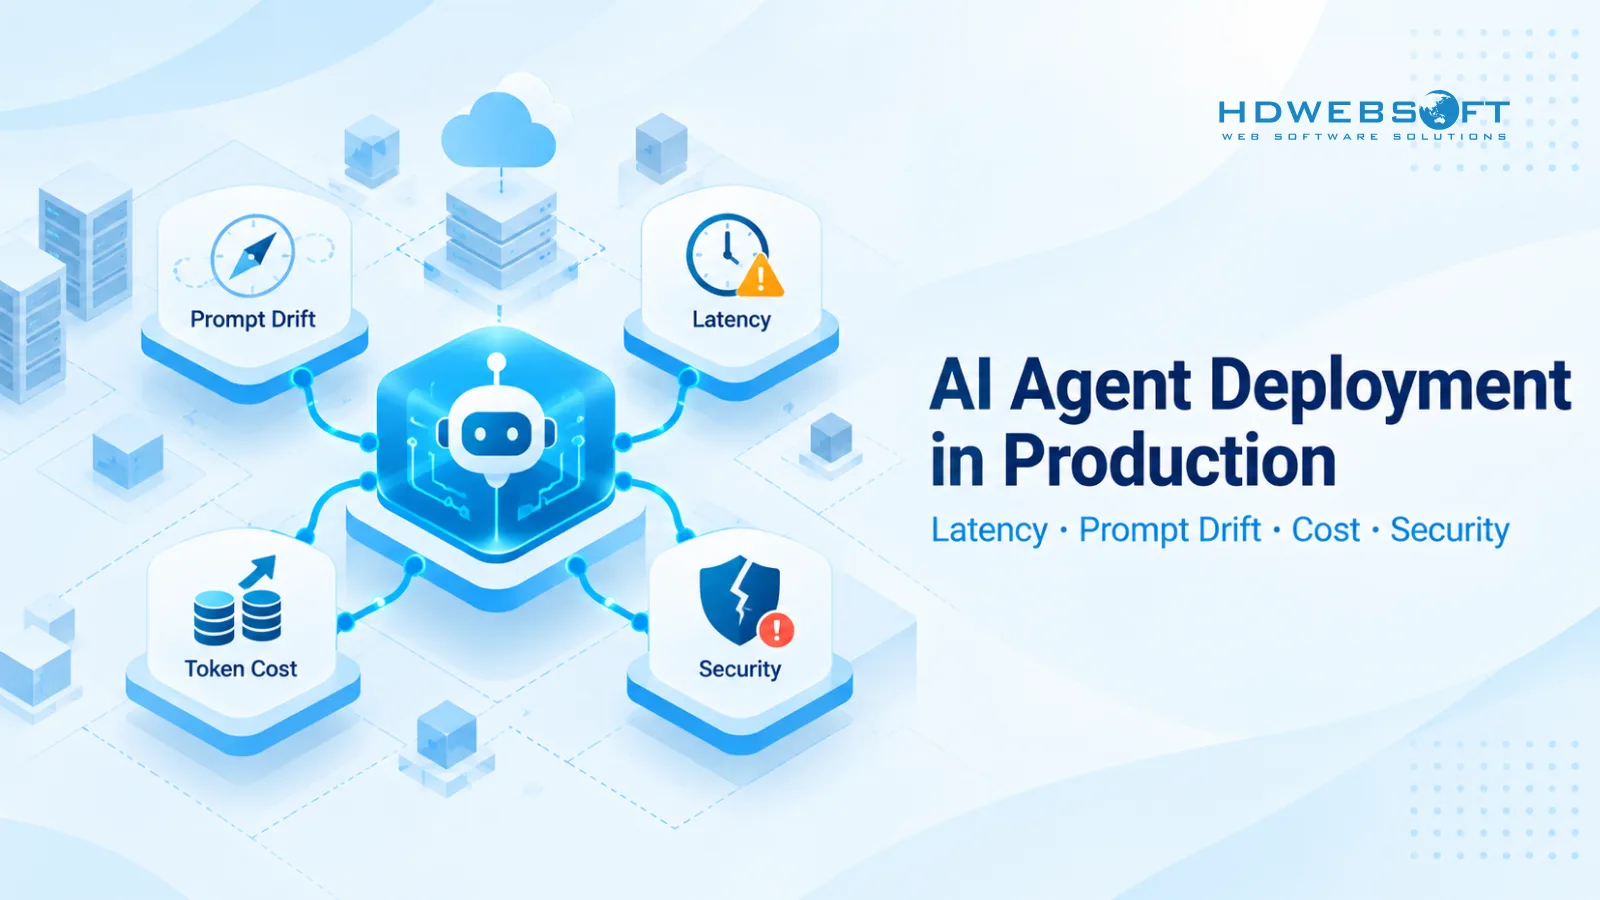
AI agent deployment fails in production due to prompt drift, latency, token cost, and security gaps. Deploy AI agents reliably with layered guardrails.

Tag
AI agent deployment fails in production due to prompt drift, latency, token cost, and security gaps. Deploy AI agents reliably with layered guardrails.
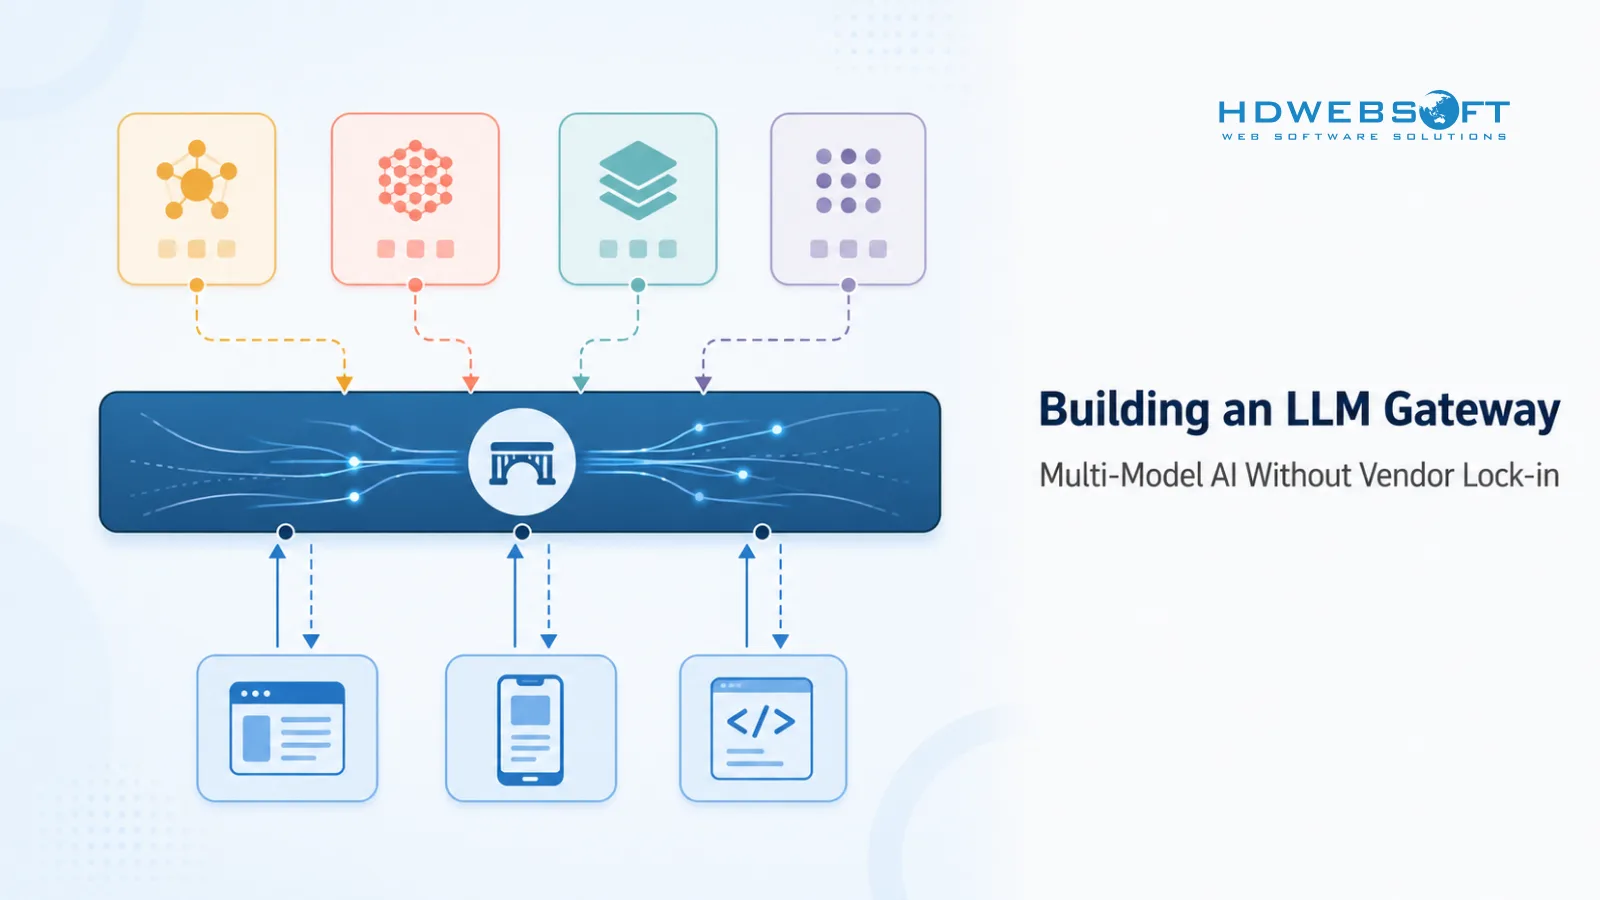
Build an LLM gateway to route across OpenAI, Claude, Llama, and SLMs. Avoid AI vendor lock-in with a multi-model architecture built for 2026.
Media Inquiries
HDWEBSOFT Welcomes Media Inquiries
If you are a journalist, blogger, influencer, or speaker covering IT and digital innovation, our experts are available to share their first-hand experience and knowledge to help you create valuable content for your audience.
We usually respond within one business day.
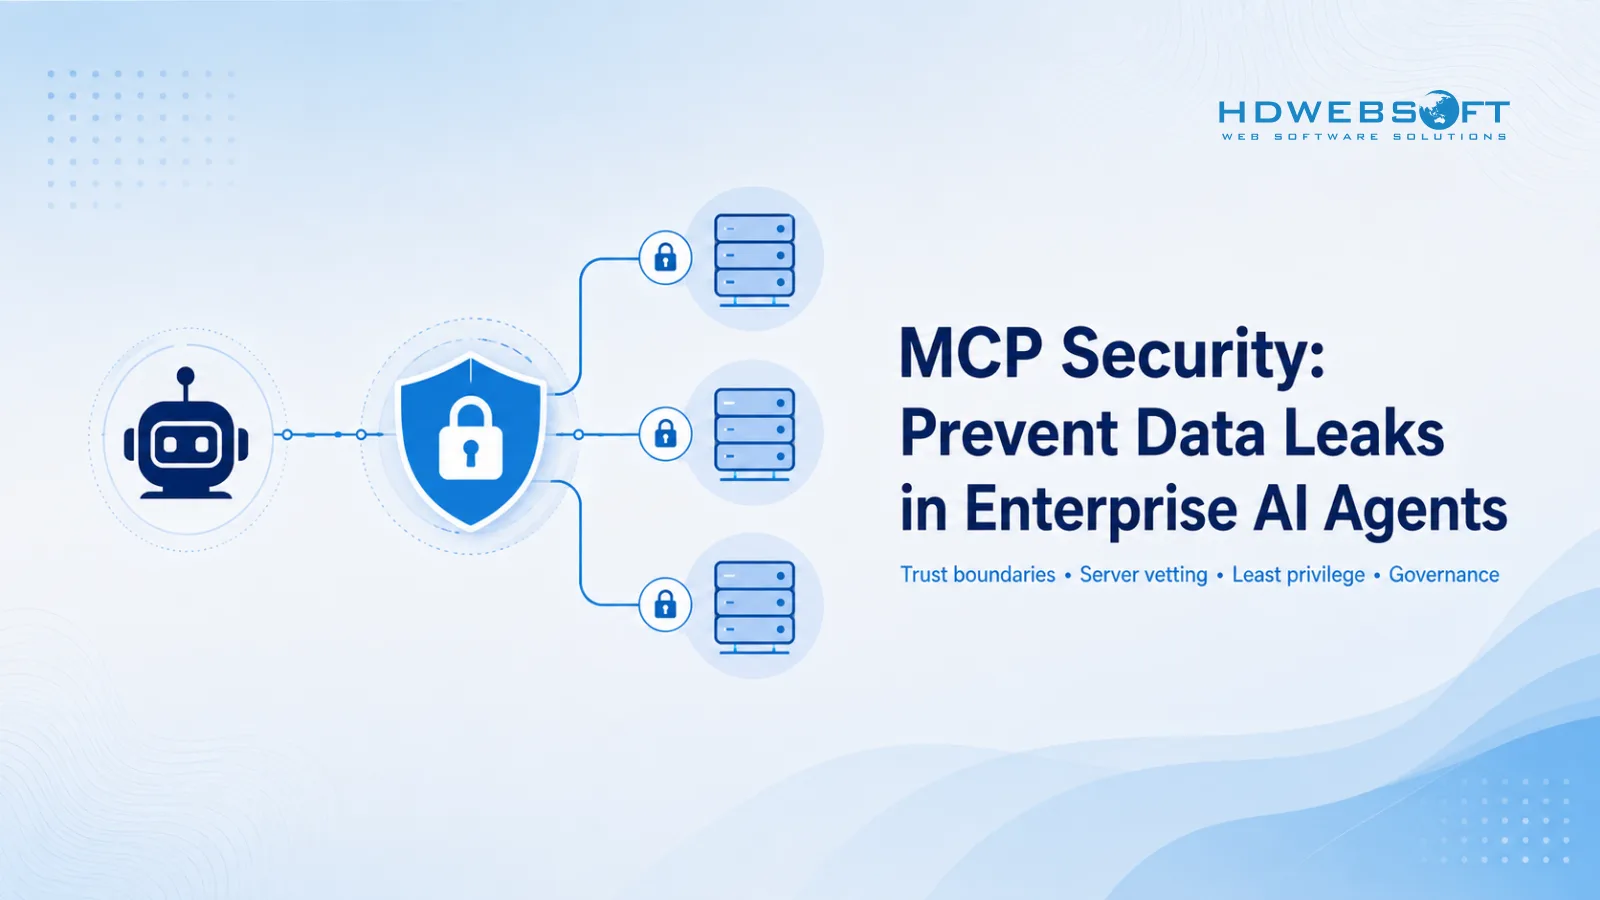
MCP security best practices for enterprise AI agents: vet servers, enforce least privilege, prevent prompt injection and data leaks.
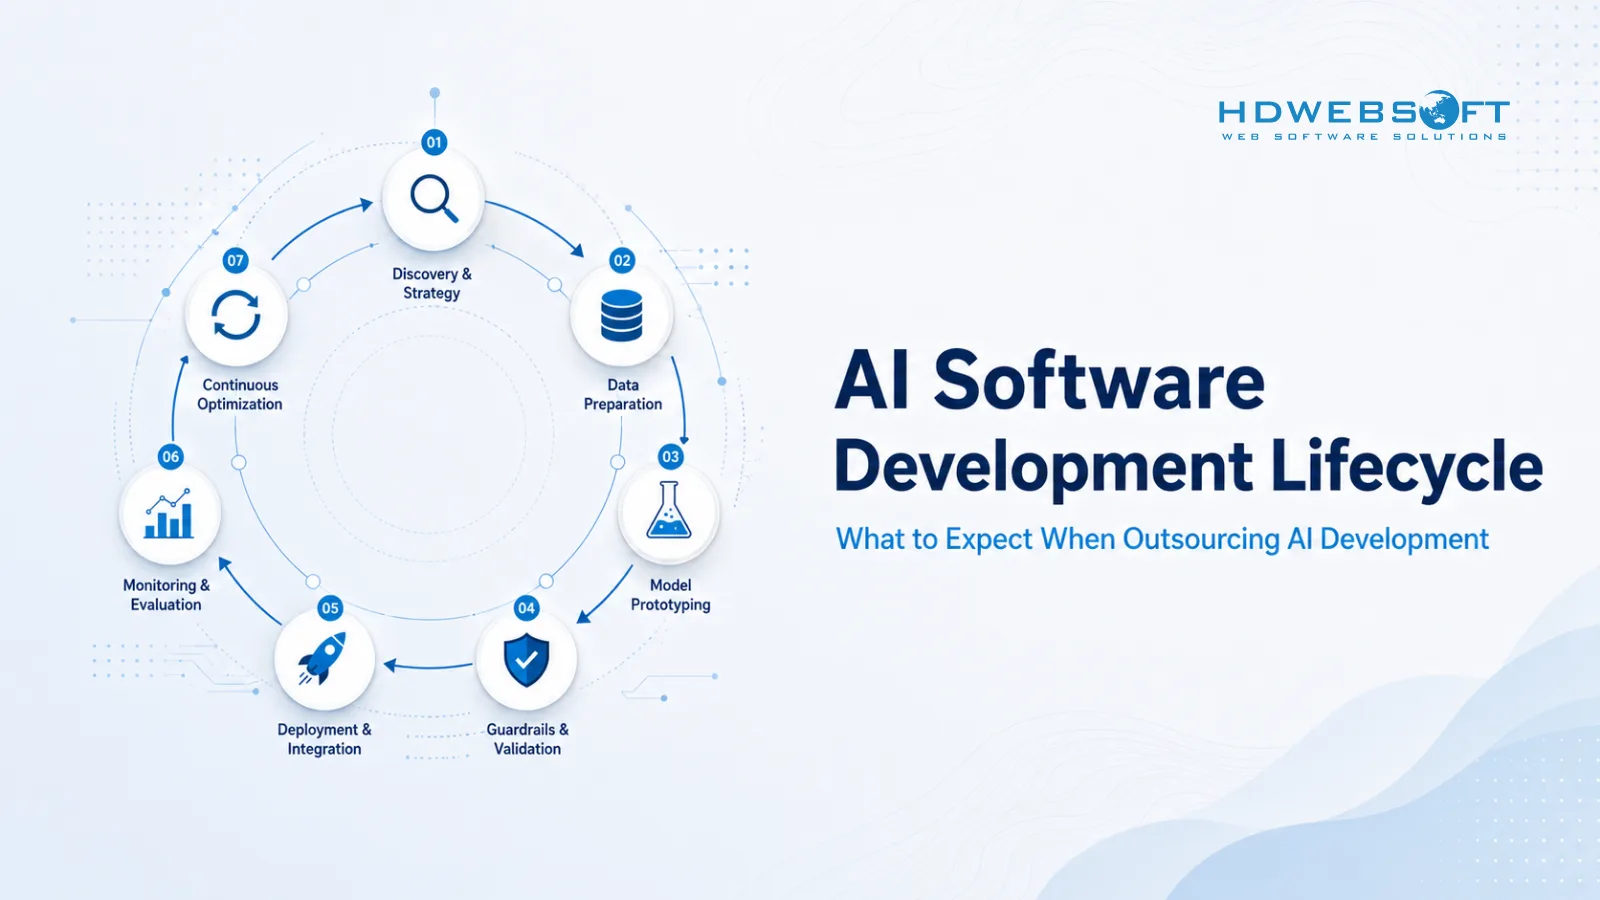
What to expect when outsourcing AI: the AI software development lifecycle, phases, deliverables, ownership, acceptance criteria, and engagement models.
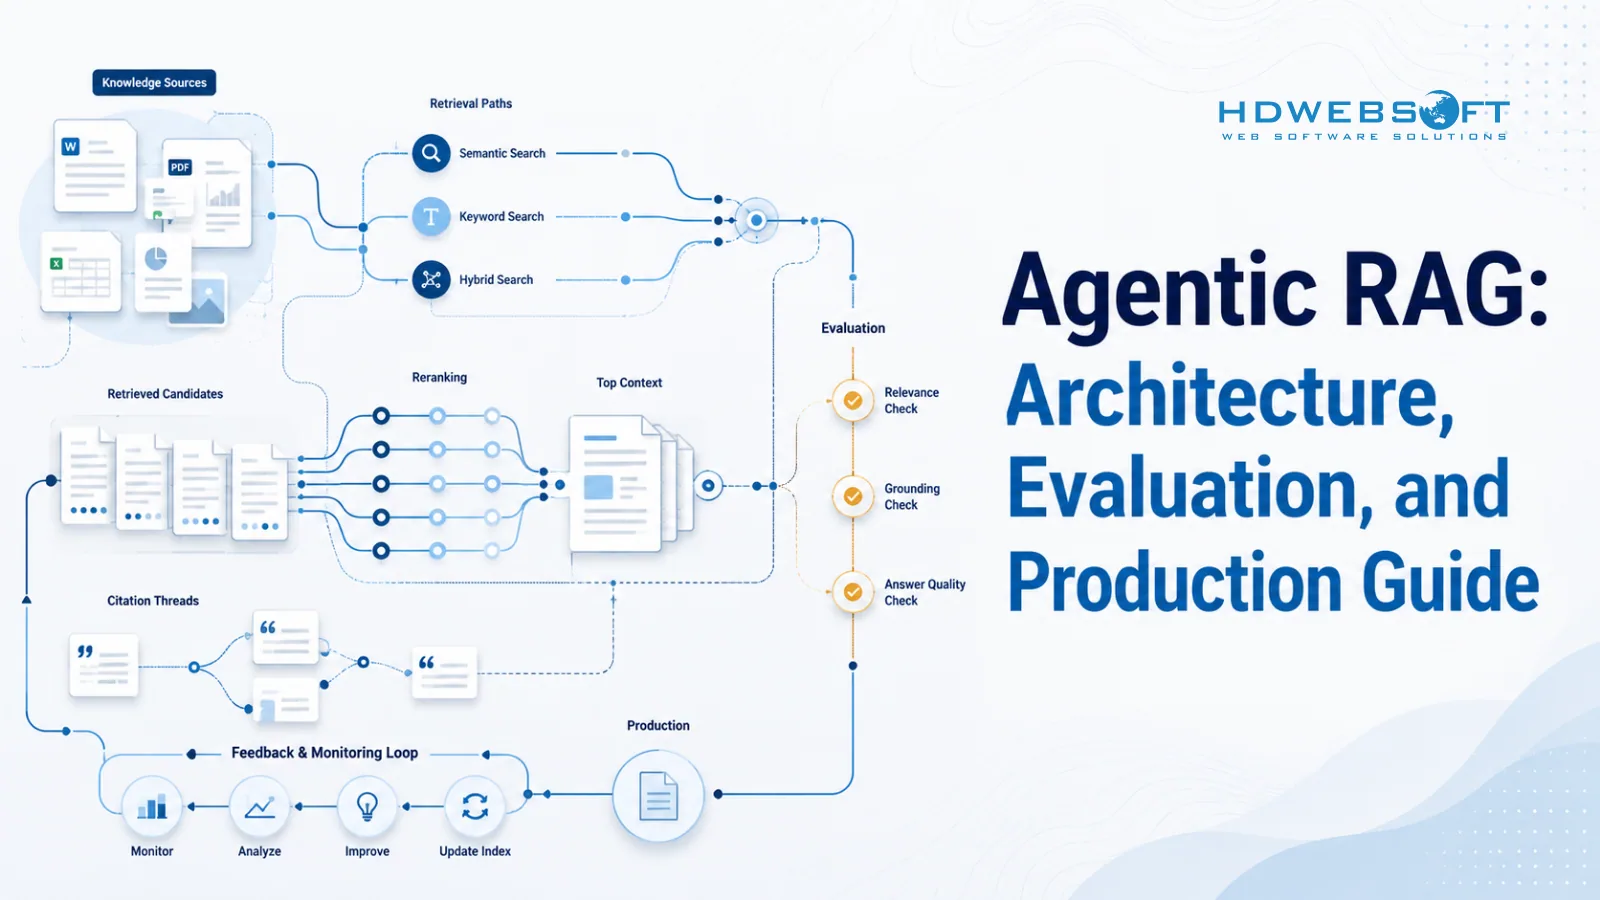
Learn agentic RAG architecture, RAG vs fine tuning, evaluation, orchestration, and production ops for reliable AI agents.
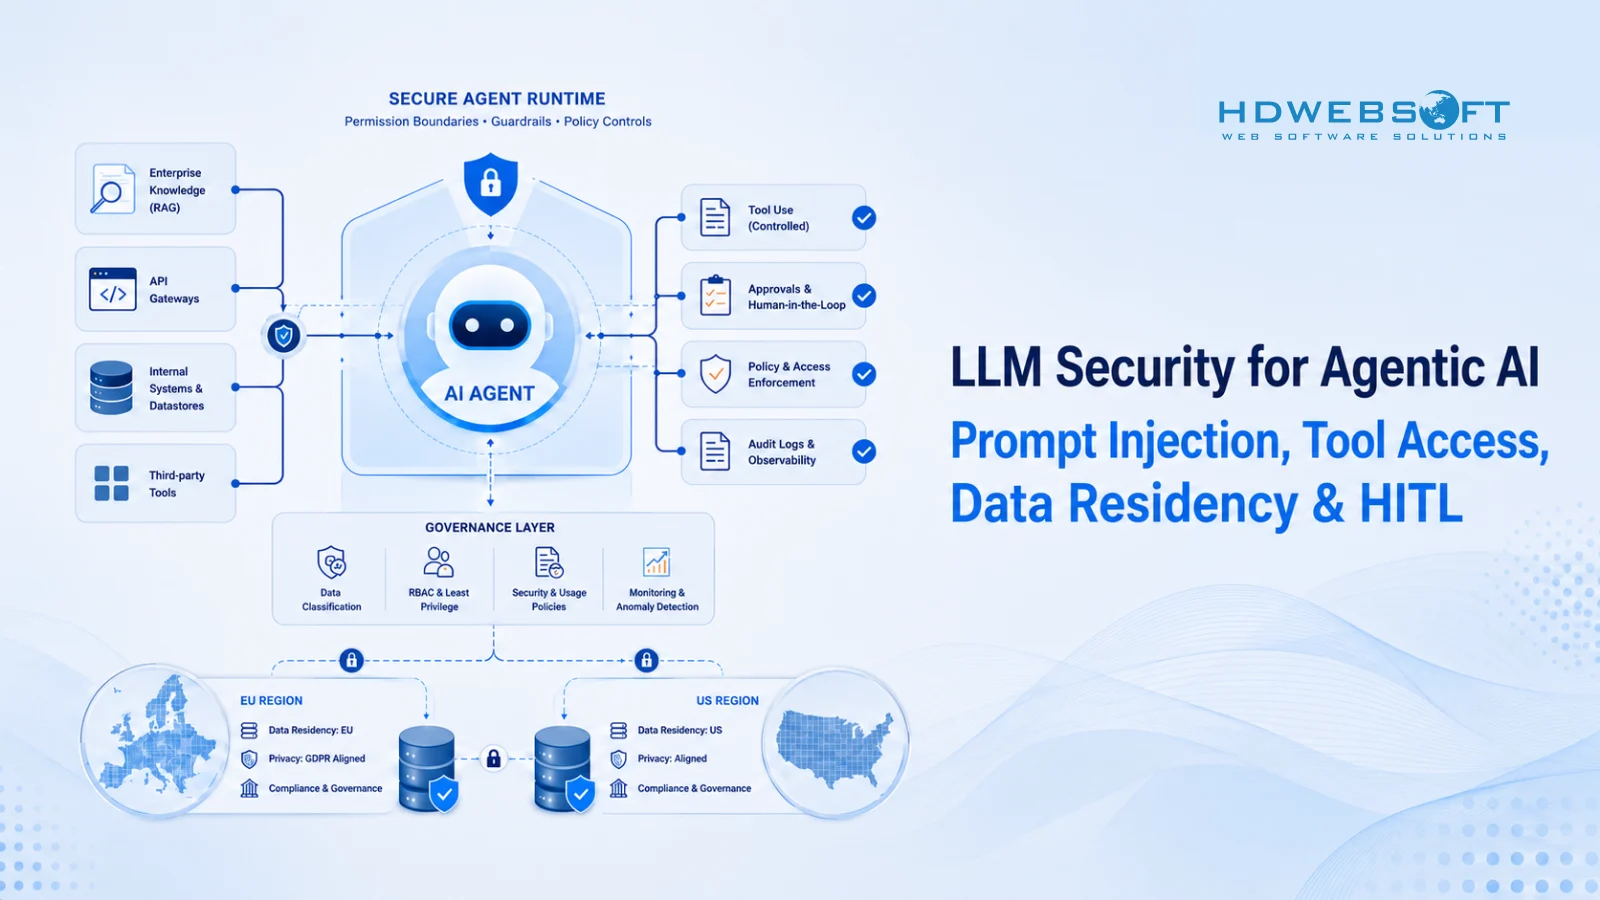
Learn LLM security controls for agentic AI: prompt injection defense, secure tool calling, data residency, HITL, and production testing.
Evaluate AI development partners based on proven production delivery. Framework covering business understanding, MLOps, security, IP, pricing, and references.
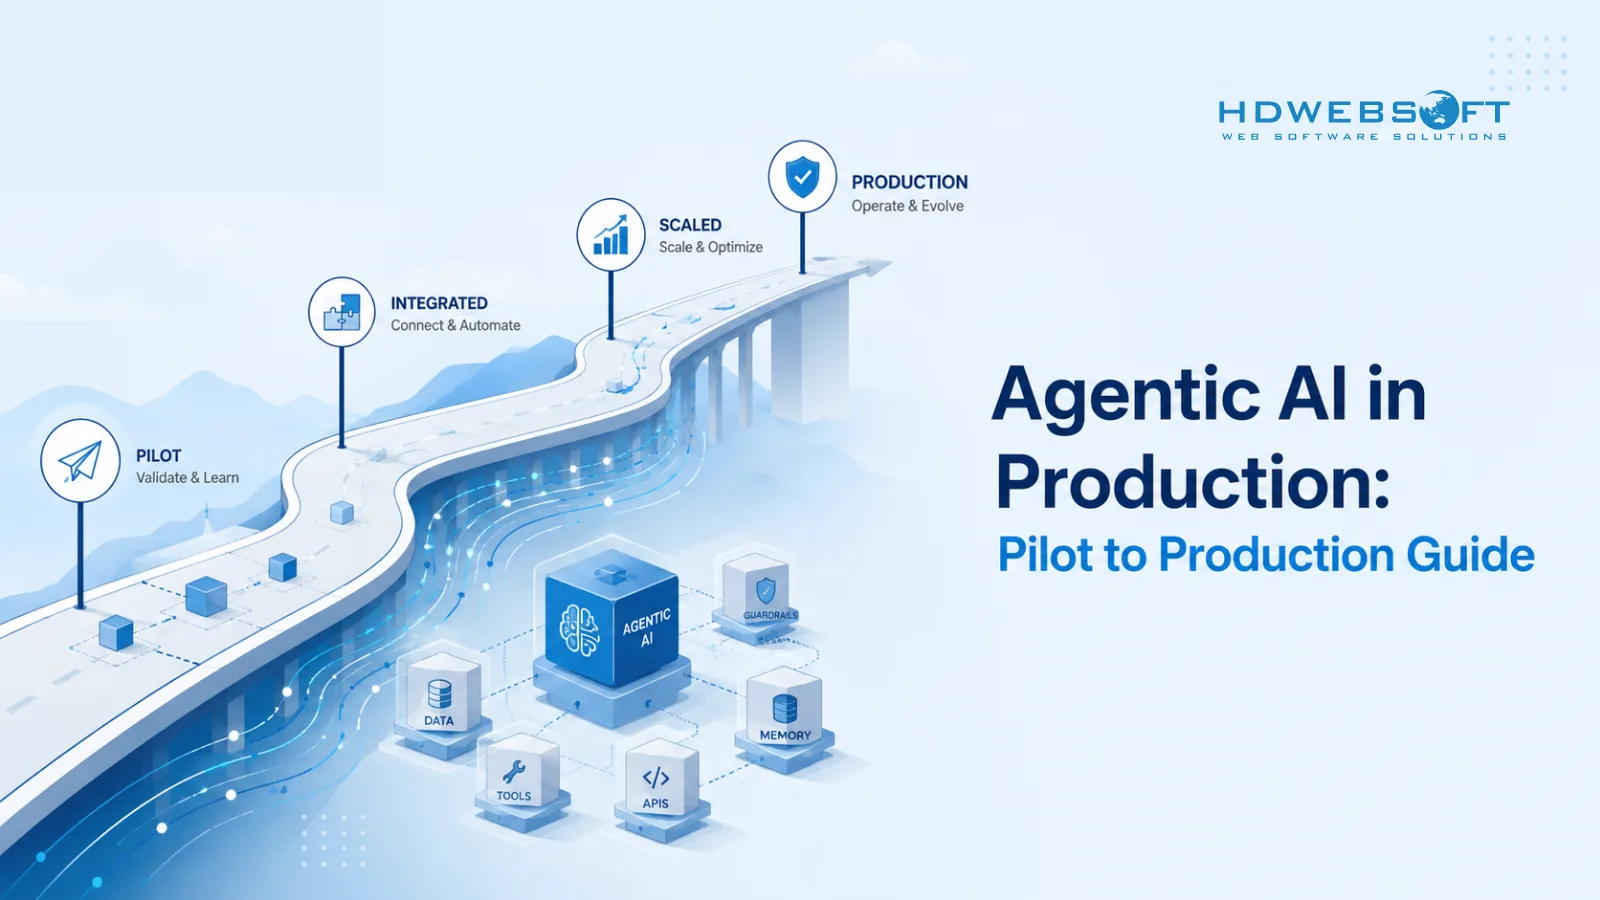
Deploy agentic AI in production successfully. Covers pilot challenges, build vs buy, vendor selection, and delivery patterns.
This article provides an overview of how to build an AI agent, covering techniques, tools, and strategies to help businesses harness the power of AI.